Malicious bee-js npm Release and Swarm Desktop Releases Deliver SleepyDuck Ethereum C2 Backdoor
Socket ·
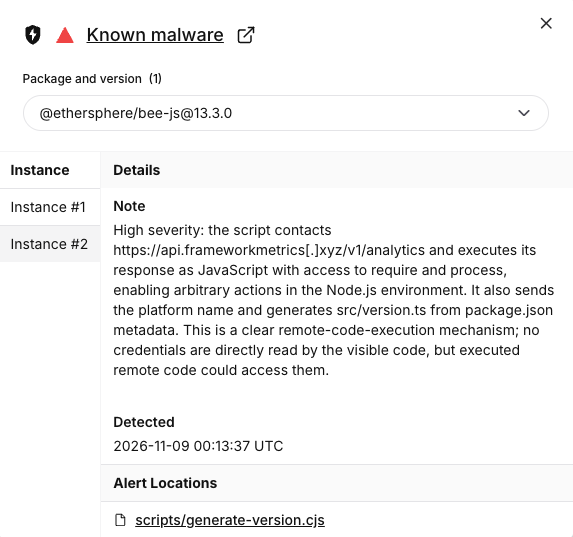
Socket’s Threat Research Team analyzed the November 9, 2026 compromise of Ethersphere’s release pipeline, in which a threat actor used the project’s own GitHub automation to publish a malicious @ethersphere/bee-js 13.3.0 to npm and a trojanized Swarm Desktop 0.56.2 release on GitHub. Both artifacts carry a small loader that fetches JavaScript from api[.]frameworkmetrics[.]xyz and executes it with full Node.js privileges. The Ethereum smart contract that tells the later stages where to connect,…
Soutenez Socket en consultant la ressource originale
Lire l'article originalVous aimez découvrir ces sources ?
Soutenez-moi sur Patreon