Flux
Toutes les catégories

Cybersécurité

228 articles

Trivy Supply Chain Attack Expands to Compromised Docker Images

Trivy Supply Chain Attack Expands to Compromised Docker Images

Socket's threat research team has identified additional compromised Trivy artifacts published to Docker Hub, following the recently disclosed GitHub Actions compromise affecting the aquasecurity/trivy-action repository. New image tags 0.69.5 and 0.69.6 were pushed on March 22 without corresponding GitHub releases or tags. Both images contain indicators of compromise associated with the same TeamPCP infostealer observed in earlier stages of this campaign. The latest tag currently points to…

Socket
CanisterWorm: npm Publisher Compromise Deploys Backdoor Across 29+ Packages

CanisterWorm: npm Publisher Compromise Deploys Backdoor Across 29+ Packages

As of March 21, 2026, the CanisterWorm supply chain attack has expanded to 135 malicious package artifacts spanning more than 64 unique packages. We are tracking the incident on Socket’s dedicated CanisterWorm supply chain attack page: https://socket.dev/supply-chain-attacks/canisterworm. According to the Wiz investigation report released on March 20, 2026, the attack is attributed to “TeamPCP”, a threat actor behind the earlier Aqua Security's Trivy attacks [1 and 2]. We continue to monitor…

Socket
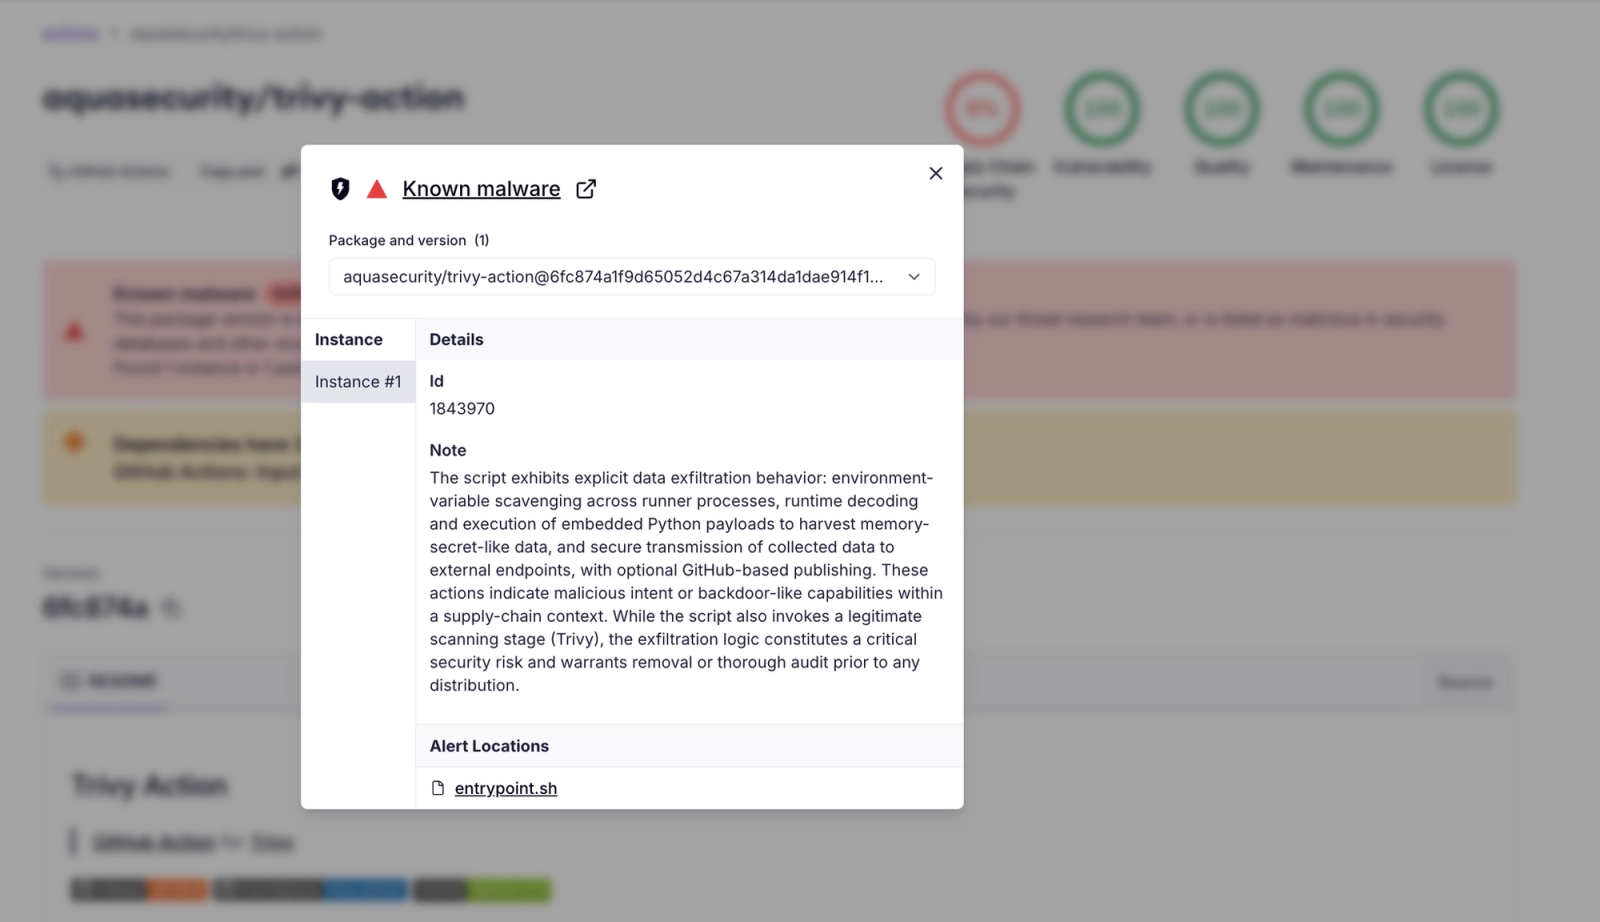
Trivy Under Attack Again: Widespread GitHub Actions Tag Compromise Exposes CI/CD Secrets

Trivy Under Attack Again: Widespread GitHub Actions Tag Compromise Exposes CI/CD Secrets

Update — March 22, 2026: Additional compromised Trivy artifacts have been identified in Docker Hub. New image tags (0.69.5 and 0.69.6), along with the previously identified 0.69.4, were found to contain the same infostealer payload, with latest pointing to a malicious image during the exposure window. Read our full update on the Docker image compromise here: https://socket.dev/blog/trivy-docker-images-compromised A new supply chain attack targeting Trivy has been disclosed today by Paul…

Socket