Flux
Toutes les catégories

Programmation

3255 articles

★ Searching multiple columns with one URL parameter in laravel-query-builder

★ Searching multiple columns with one URL parameter in laravel-query-builder

We just released v7.3.0 of laravel-query-builder, which adds a new way to group multiple filters under a single URL parameter. Before getting into the new feature, let me show you how the basics work, so the new bit makes sense in context. The basics Here's a typical setup in a controller: use Spatie\QueryBuilder\AllowedFilter; use Spatie\QueryBuilder\QueryBuilder; $users = QueryBuilder::for(User::class) ->allowedFilters( AllowedFilter::partial('name'), AllowedFilter::exact('status'), )…

Freek Van der Herten
Quoting Anthropic

Quoting Anthropic

We used an automatic classifier which judged sycophancy by looking at whether Claude showed a willingness to push back, maintain positions when challenged, give praise proportional to the merit of ideas, and speak frankly regardless of what a person wants to hear. Most of the time in these situations, Claude expressed no sycophancy—only 9% of conversations included sycophantic behavior (Figure 2). But two domains were exceptions: we saw sycophantic behavior in 38% of conversations focused on…

Simon Willison's Weblog
Sightings

Sightings

/elsewhere/sightings/ I have a new camera (a Canon R6 Mark II) so I'm taking a lot more photos of birds. I share my best wildlife photos on iNaturalist, and based on yesterday's successful prototype I decided to add those to my blog. I built this feature on my phone using Claude Code for web, as an extension of my beats system for syndicating external content. Here's the PR and prompt. As with my other forms of incoming syndicated content sightings show up on the homepage, the date archive…

Simon Willison's Weblog
PyPI Fixes High-Severity Access Control Issues Found in Security Audit

PyPI Fixes High-Severity Access Control Issues Found in Security Audit

PyPI has fixed two high-severity flaws found during its second external security audit, addressing access control issues that could have allowed organization members to invite new owners and stale team permissions to persist after project transfers. The audit was performed by Trail of Bits and funded by the Sovereign Tech Agency. It reviewed Warehouse, the open source Python application that powers PyPI and handles package uploads, metadata validation, storage, and downloads for pip and other…

Socket
iNaturalist Sightings

iNaturalist Sightings

Tool: iNaturalist Sightings I wanted to see my iNaturalist observations - across two separate accounts - grouped by when they occurred. I'm camping this weekend so I built this entirely on my phone using Claude Code for web. I started by building an inaturalist-clumper Python CLI for fetching and "clumping" observations - by default clumps use observations within 2 hours and 5km of each other. Then I setup simonw/inaturalist-clumps as a Git scraping repository to run that tool and record the…

Simon Willison's Weblog
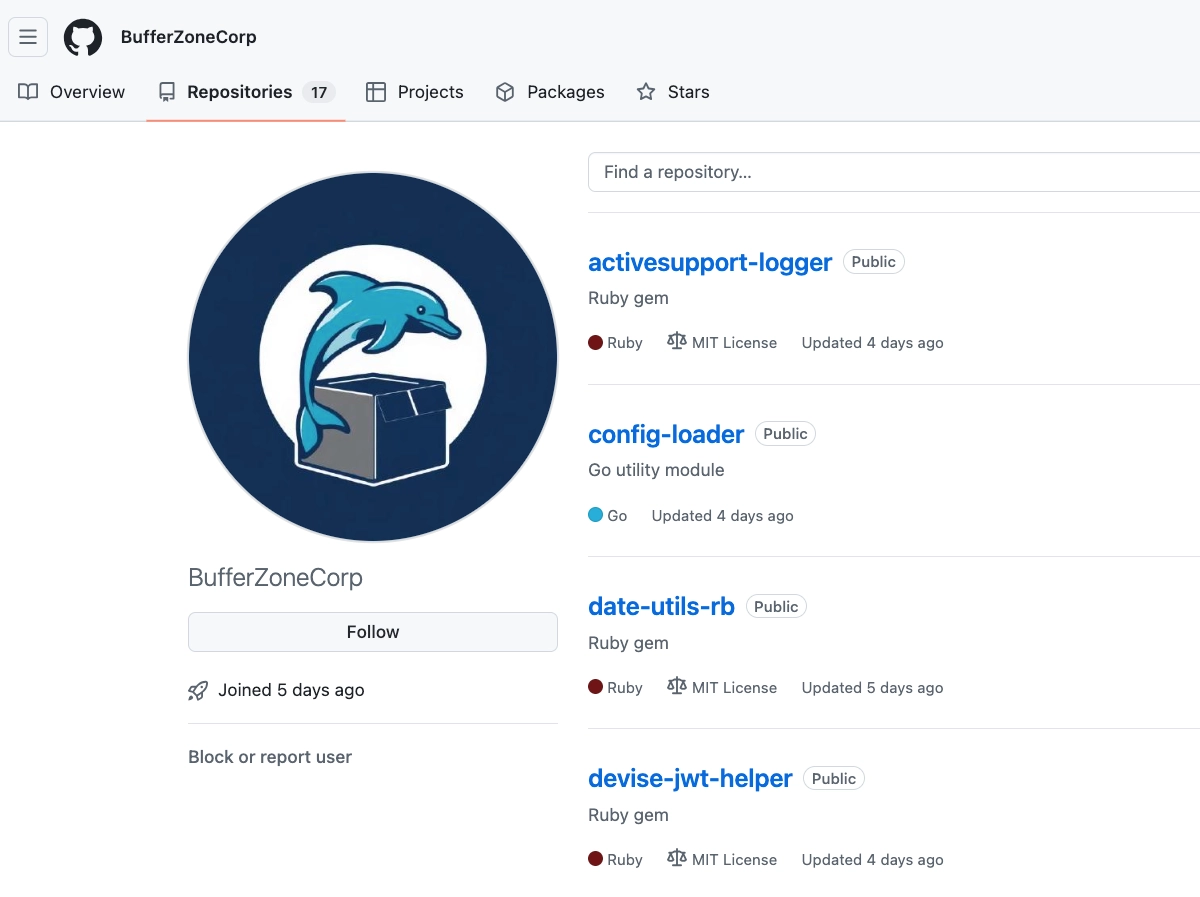
Malicious Ruby Gems and Go Modules Impersonate Developer Tools to Steal Secrets and Poison CI

Malicious Ruby Gems and Go Modules Impersonate Developer Tools to Steal Secrets and Poison CI

We investigated the GitHub account BufferZoneCorp, which published a cluster of repositories linked to malicious Ruby gems and Go modules. The account is part of a software supply chain campaign targeting developers, CI runners, and build environments across two ecosystems. On the Ruby side, the analyzed gems automate secret theft. They harvest secret-bearing environment variables and read local credential material such as SSH keys, AWS credentials, .npmrc, .netrc, GitHub CLI configuration, and…

Socket
Codex CLI 0.128.0 adds /goal

Codex CLI 0.128.0 adds /goal

Codex CLI 0.128.0 adds /goal The latest version of OpenAI's Codex CLI coding agent adds their own version of the Ralph loop: you can now set a /goal and Codex will keep on looping until it evaluates that the goal has been completed... or the configured token budget has been exhausted. It looks like the feature is mainly implemented though the goals/continuation.md and goals/budget_limit.md prompts, which are automatically injected at the end of a turn. Via @fcoury Tags: ai, openai,…

Simon Willison's Weblog
Our evaluation of OpenAI's GPT-5.5 cyber capabilities

Our evaluation of OpenAI's GPT-5.5 cyber capabilities

Our evaluation of OpenAI's GPT-5.5 cyber capabilities The UK's AI Security Institute previously evaluated Claude Mythos: now they've evaluated GPT-5.5 for finding security vulnerability and found it to be comparable to Mythos, but unlike Mythos it's generally available right now. Tags: ai, openai, generative-ai, llms, anthropic, claude, ai-security-research, gpt

Simon Willison's Weblog