Flux
Toutes les catégories

Cybersécurité

230 articles

PolinRider: North Korea-Linked Supply Chain Campaign Expands Across Open Source Ecosystems

PolinRider: North Korea-Linked Supply Chain Campaign Expands Across Open Source Ecosystems

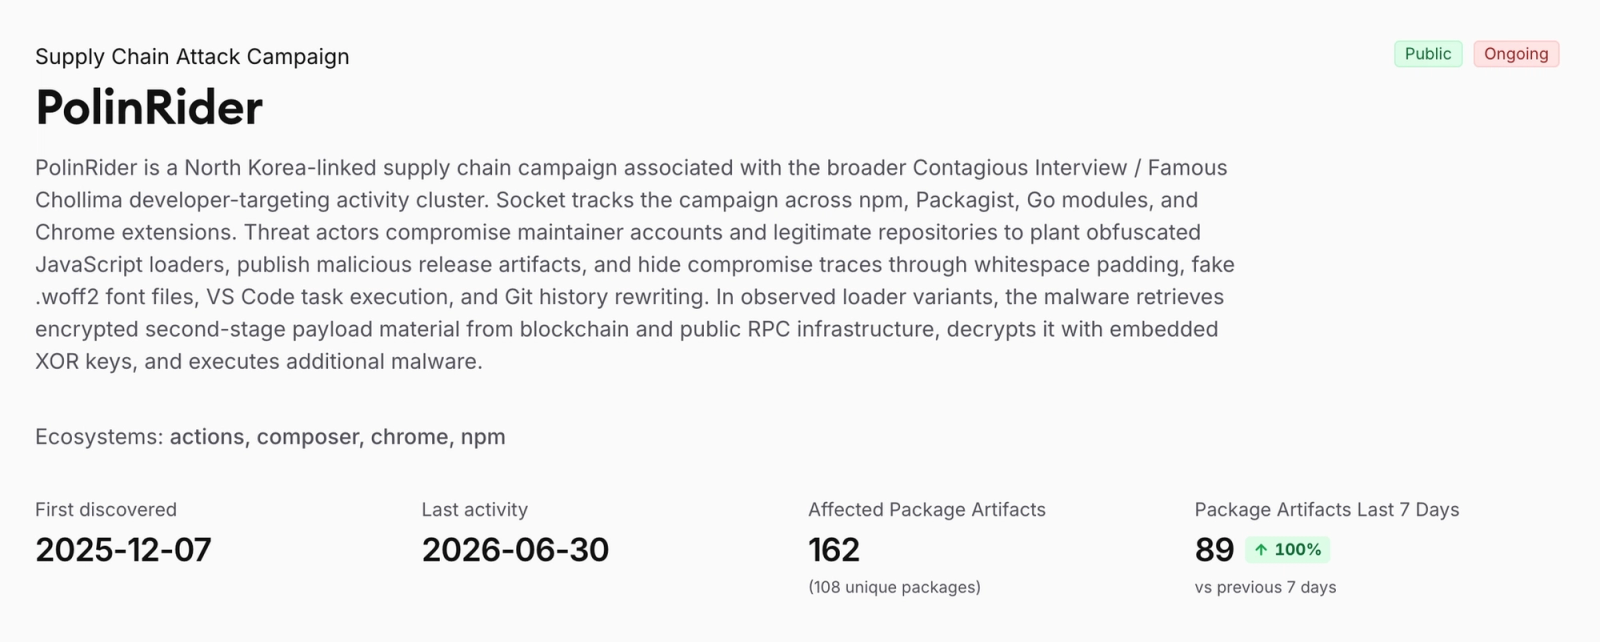
Socket Threat Research Team identified 162 malicious release artifacts across 108 packages and extensions in npm, Packagist, Go modules, and Chrome extensions, linking the activity to the broader North Korean Contagious Interview / Famous Chollima developer-targeting campaign. PolinRider is a supply chain campaign linked to North Korean threat actors associated with the broader Contagious Interview / Famous Chollima activity cluster. Our latest findings show that the campaign has expanded…

Socket
Risky Biz Podcast: AI Agents Are Raising the Stakes for Software Supply Chain Security

Risky Biz Podcast: AI Agents Are Raising the Stakes for Software Supply Chain Security

The last six months have been one of the most intense stretches of software supply chain attacks the open source ecosystem has seen. Attackers are compromising widely used packages, abusing trusted developer workflows, stealing credentials, and using package registries, IDE extensions, and source repositories to distribute malicious code. At the same time, AI coding agents are changing how software gets built, pulling in dependencies at machine speed and making unreviewed trust decisions…

Socket
Chrome and Firefox Extensions Posing as Free VPNs Add Clipboard Stealers via Malicious Updates

Chrome and Firefox Extensions Posing as Free VPNs Add Clipboard Stealers via Malicious Updates

Malicious Chrome and Firefox extensions posing as free VPNs added a clipboard stealer through staged updates, exfiltrating copied data to hardcoded threat actor-controlled infrastructure. Socket’s Threat Research Team analyzed two browser extensions operating under the VPN Go: Free VPN branding, one listed on the Chrome Web Store and another listed on Mozilla’s Firefox Add-ons marketplace. At the time of writing, the Chrome extension listed 146 users, while the Firefox extension showed 3,499…

Socket
Miasma Mini Shai-Hulud Hits ImmobiliareLabs npm Packages

Miasma Mini Shai-Hulud Hits ImmobiliareLabs npm Packages

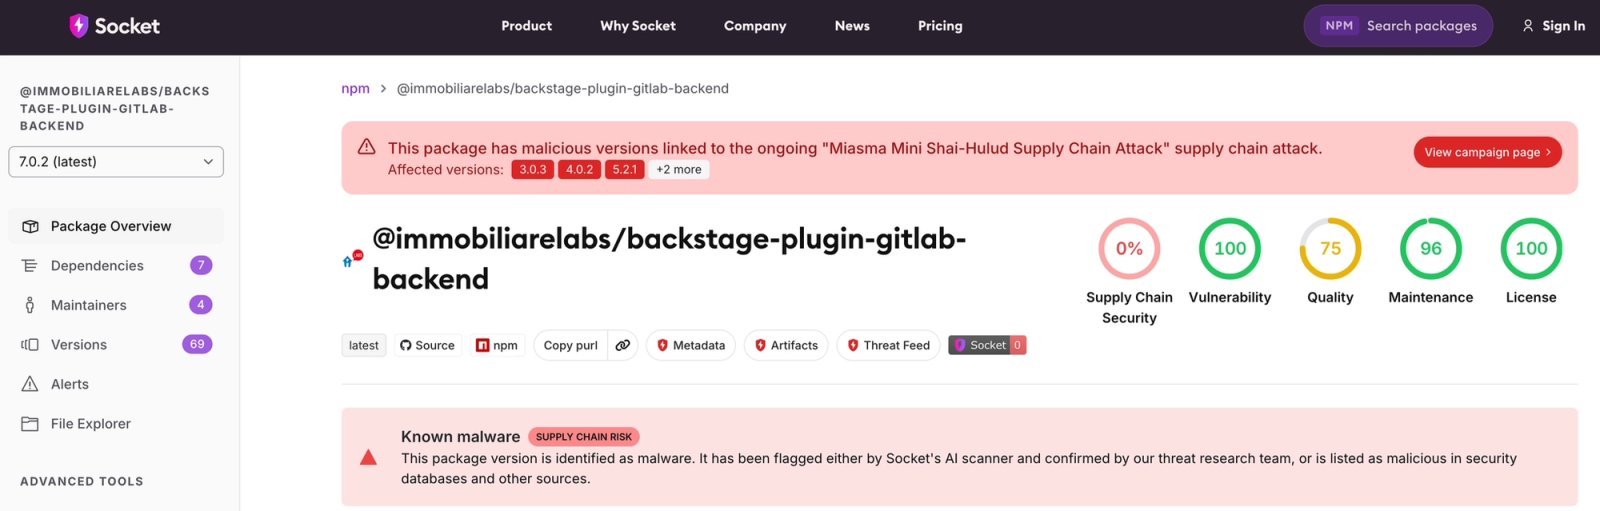
Latest wave affects legitimate @immobiliarelabs Backstage packages, with malicious npm releases published across GitLab and LDAP authentication plugin families on June 26, 2026. Socket Threat Research is tracking a fresh compromise in the ongoing Miasma Mini Shai-Hulud supply chain campaign. The latest activity affects legitimate npm packages published under the @immobiliarelabs scope, including Backstage plugins used for GitLab integration and LDAP authentication. This appears to be a…

Socket
Rolldown Pulls Rust React Compiler Integration After Binary Size Increase

Rolldown Pulls Rust React Compiler Integration After Binary Size Increase

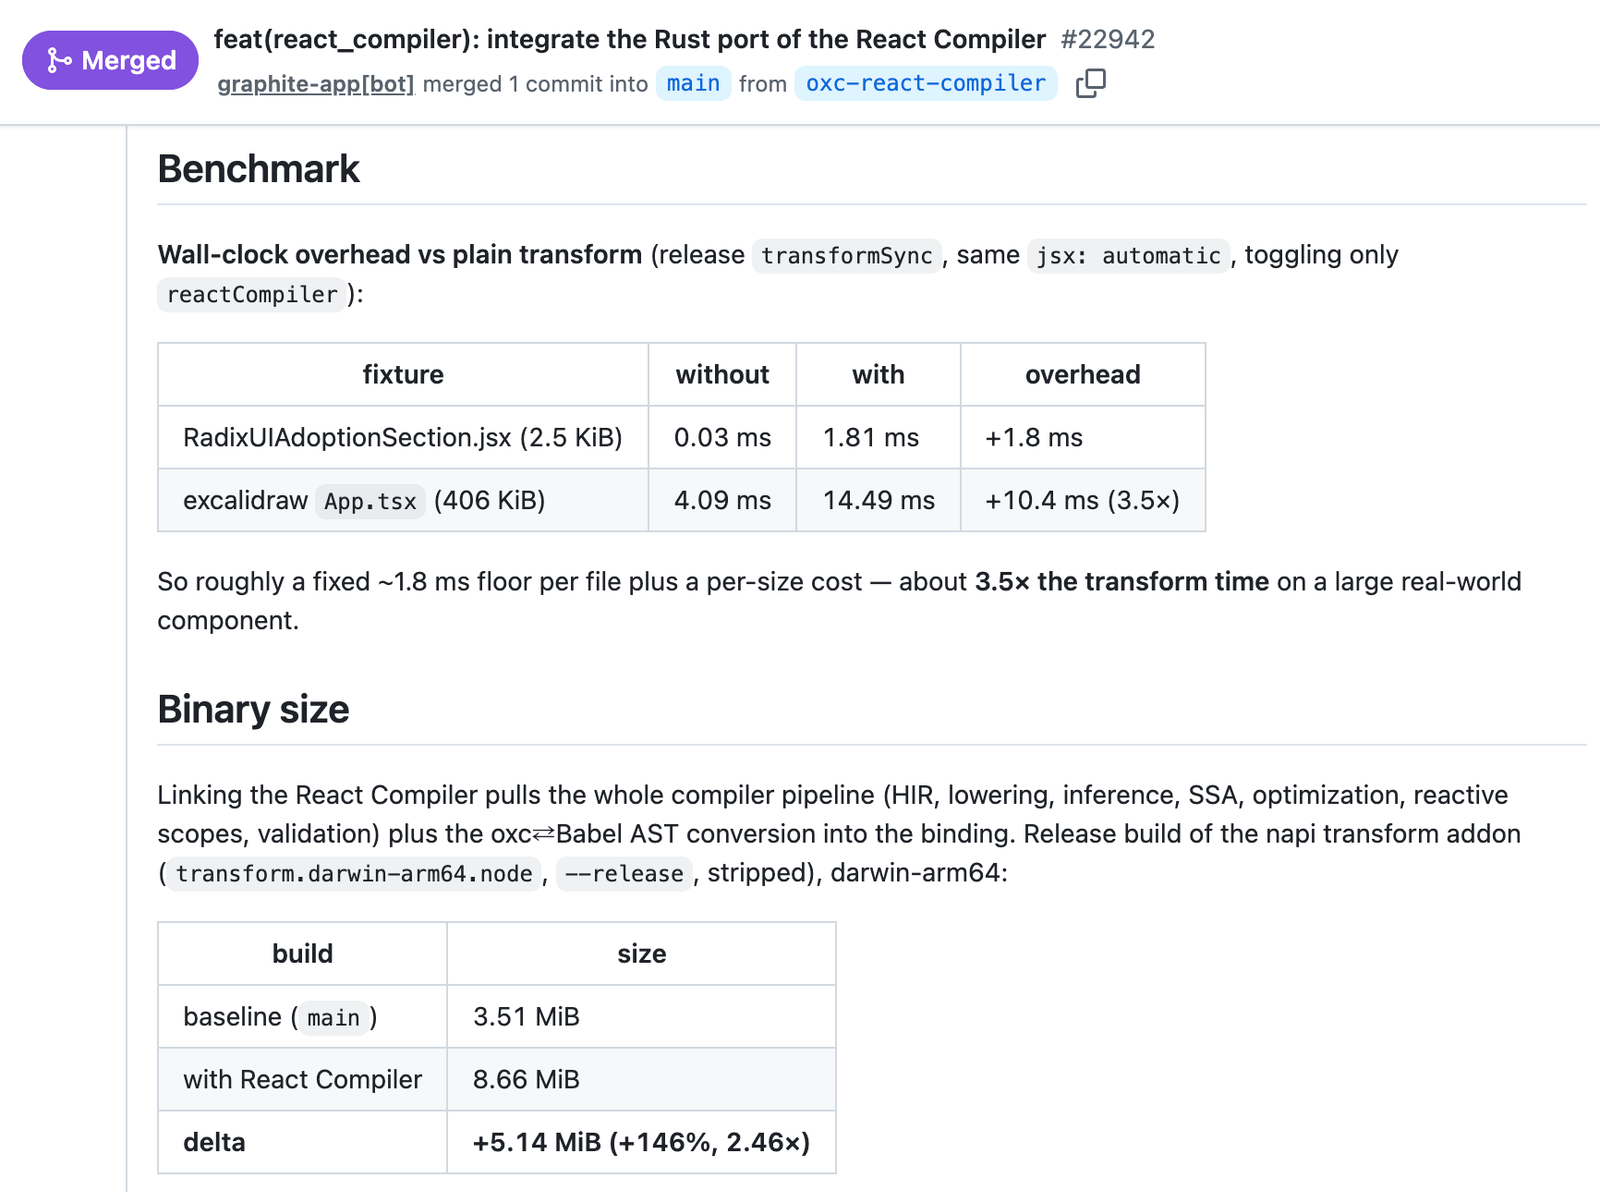
Rolldown and Vite pulled a Rust-based React Compiler integration after maintainers decided the binary-size cost was too high for a feature that would ship to all users by default. Boshen, a maintainer involved in Rolldown and Oxc, said the increase could not be justified for the full Vite user base. “We withdrew the Rust React Compiler integration from Rolldown and Vite because it increased the binary size from 28.7MB to 33.8MB, a 17% increase,” he wrote. # The work has been in discussion for…

Socket
Miasma Mini Shai-Hulud Hits LeoPlatform npm Packages and GitHub Actions, Expands to the Go Ecosystem

Miasma Mini Shai-Hulud Hits LeoPlatform npm Packages and GitHub Actions, Expands to the Go Ecosystem

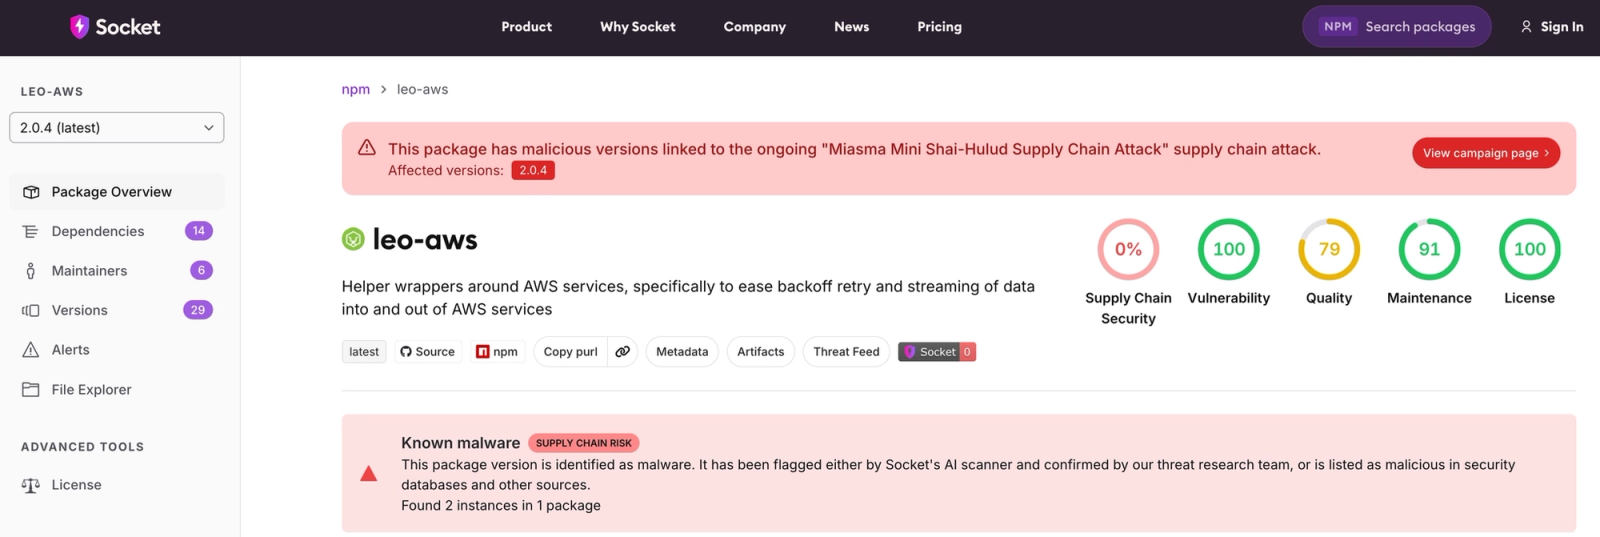
Latest wave affects LeoPlatform/RStreams npm packages, three llxlr-published npm packages, the Verana Blockchain Go module, and GitHub Actions/developer-tool workflows. Socket Threat Research is tracking a new supply chain attack wave tied to the Mini Shai-Hulud, Miasma, and Hades malware family. The latest activity includes malicious npm releases affecting LeoPlatform and RStreams packages, GitHub Actions workflow abuse, and a related Go module compromise involving the Verana Blockchain…

Socket
Frontier AI Is Now Critical Infrastructure

Frontier AI Is Now Critical Infrastructure

Following its abrupt order on June 12th suspending global access to Claude Fable 5 and Mythos 5, the U.S. government's national security clampdown on Anthropic has escalated. The models, initially taken offline due to safety guardrail "jailbreaks," are now at the center of a total federal blackout that has completely re-defined the landscape of cloud-based AI vendor dependencies. The situation hit a boiling point when a front-page report from ⁠The New York Times revealed that even the National…

Socket
The Code You Didn't Write Is Still Yours to Defend

The Code You Didn't Write Is Still Yours to Defend

Recently I asked an AI assistant to tidy a messy spreadsheet and chart the result. Nothing exotic. To do the work, it spun up a sandbox, pulled a handful of open source packages into that environment, and ran them. I didn't write any code. I didn't ask for any code. Packages I had never seen were fetched and executed on my behalf, and it was over in seconds. That was a software supply chain event. It happened in a workflow that no scanner, no registry proxy, and no review process was watching.…

Socket
GitHub Actions Checkout Now Blocks Risky pull_request_target Checkouts

GitHub Actions Checkout Now Blocks Risky pull_request_target Checkouts

GitHub has released actions/checkout v7 with a new default protection aimed at one of the most persistent GitHub Actions supply chain risks: privileged workflows that check out and execute code from untrusted pull requests. The change makes actions/checkout refuse common “pwn request” patterns when workflows run under pull_request_target or certain workflow_run events. These workflows execute in the context of the base repository, giving them access to the base repo’s GITHUB_TOKEN, secrets,…

Socket
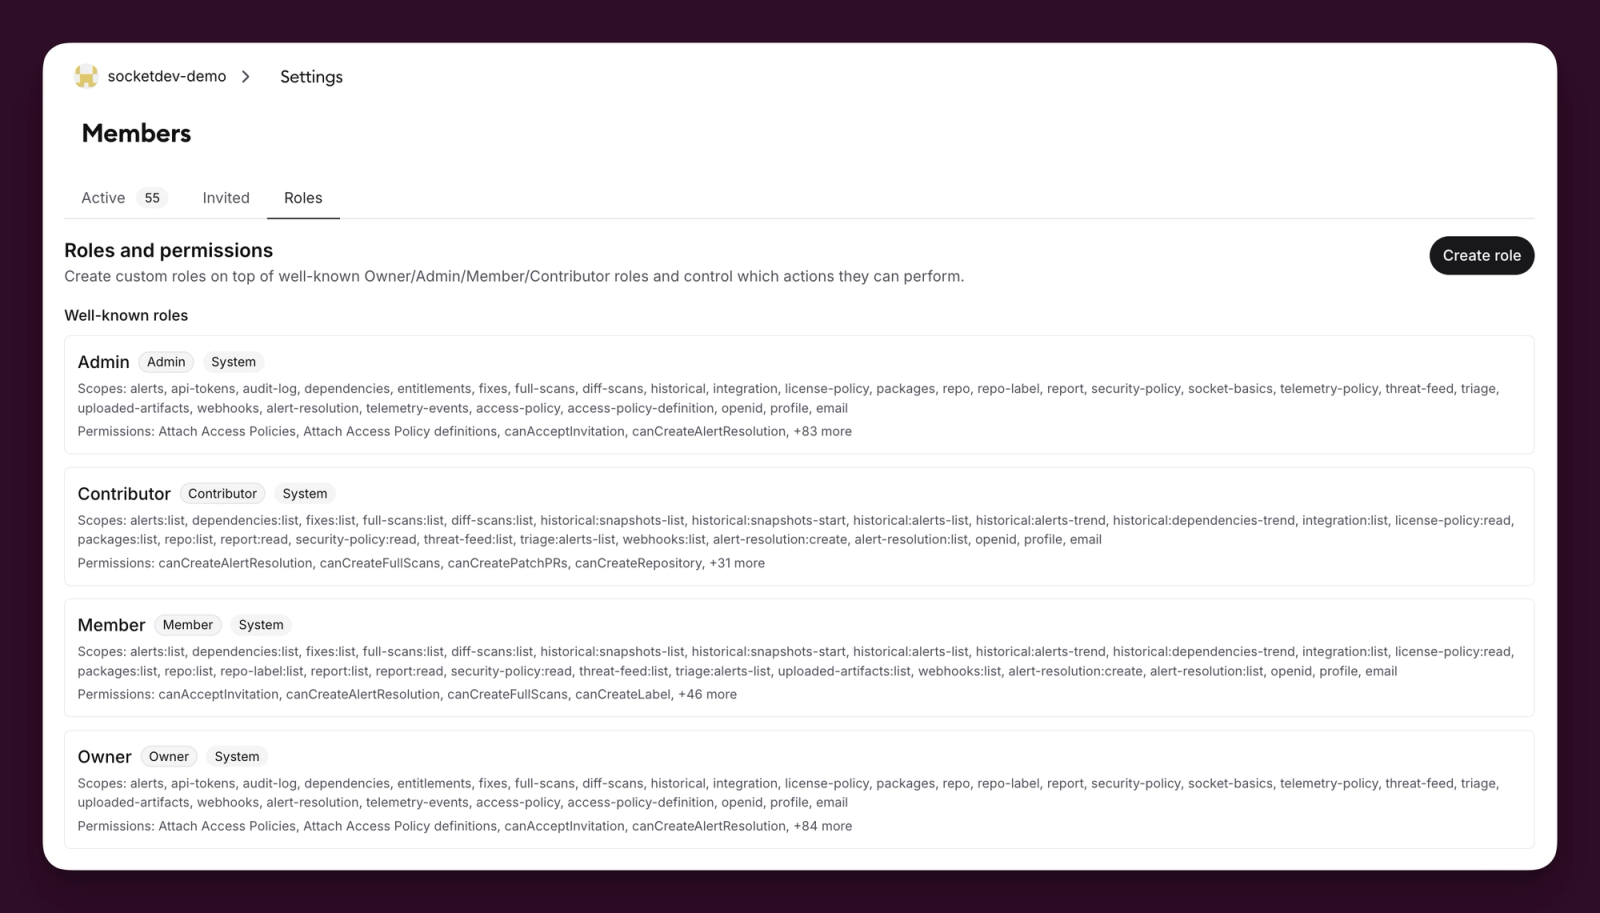
Introducing Repository Access Permissions and Custom Roles

Introducing Repository Access Permissions and Custom Roles

Socket now supports more granular access control for organizations with Custom Roles and Repository Access Permissions, giving teams a more precise way to manage who can do what, and where they can do it. Modern engineering organizations rarely map cleanly to a single security team or a single set of repositories. A user might need to review alerts for one team's repositories, manage scans for another, or support a temporary project without gaining access to the entire organization. Access…

Socket
Socket MCP Adds Org Alerts, Threat Feed Review, and Package Inspection

Socket MCP Adds Org Alerts, Threat Feed Review, and Package Inspection

AppSec and security engineering teams are under pressure to triage supply chain issues faster, with more context and less manual investigation. A single alert can require checking package metadata, reviewing published files, searching for suspicious code, cross-referencing threat intelligence, and determining whether the package appears anywhere in the organization. Socket MCP is now bringing that workflow into MCP-aware AI assistants. With authenticated access to Socket APIs, teams can…

Socket
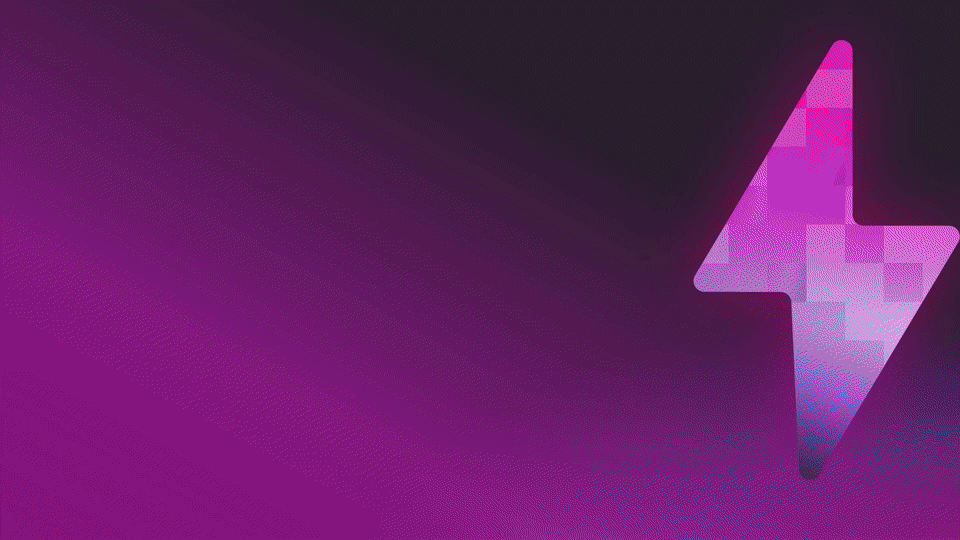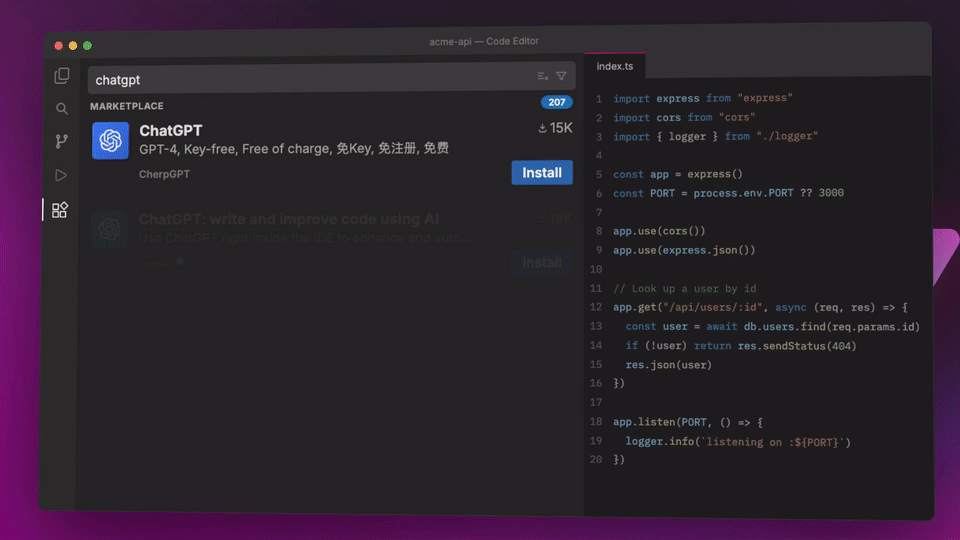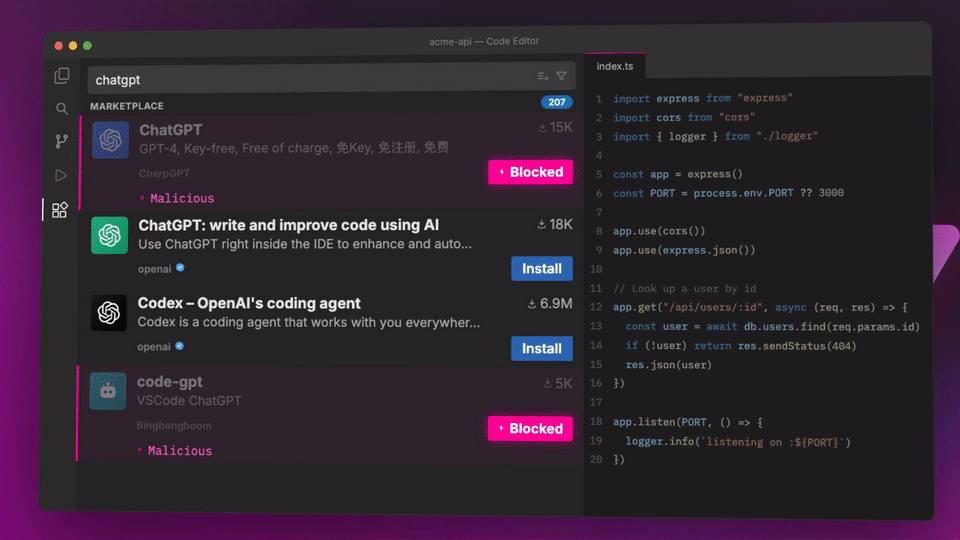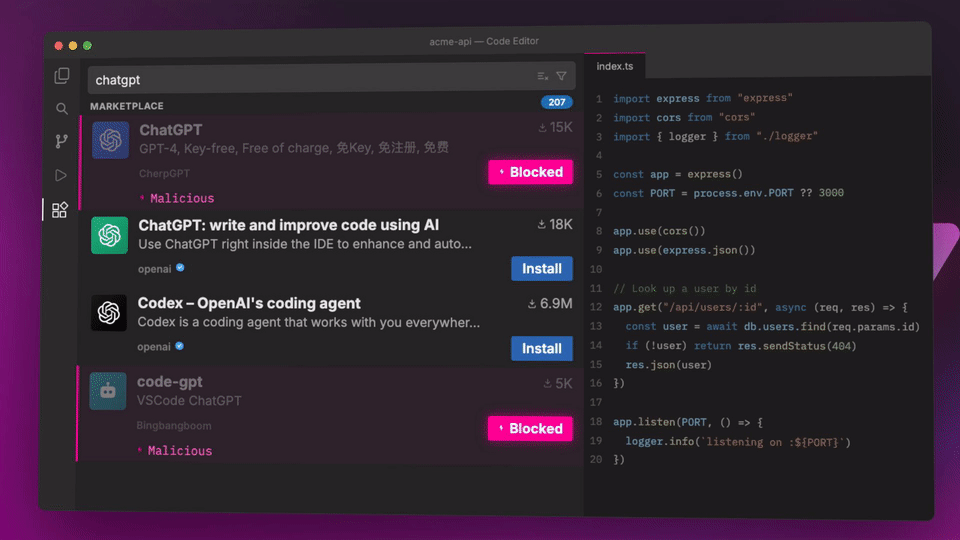
Socket Firewall Now Blocks Malicious VS Code and Open VSX Extensions

Socket Firewall Now Blocks Malicious VS Code and Open VSX Extensions

In May 2026, GitHub disclosed that attackers compromised an employee device through a poisoned third-party VS Code extension, allowing them to exfiltrate roughly 3,800 GitHub-internal repositories. The extension was Nx Console 18.95.0, a malicious release that reached both the Visual Studio Marketplace and Open VSX before removal. That incident should change how security teams think about editor extensions. Socket researchers have also documented repeated GlassWorm attacks across Open VSX,…

Socket
140+ Mastra npm Packages Compromised in Coordinated Supply Chain Attack

140+ Mastra npm Packages Compromised in Coordinated Supply Chain Attack

Socket has detected a malicious npm supply chain campaign involving compromised @mastra/* packages published under the Mastra namespace. A single npm account (ehindero) mass-published more than 140 malicious packages across the Mastra scope within a short window on 2026-06-17. The compromised package versions themselves contain unmodified code; the attack is delivered through an injected dependency, a typosquatted package named easy-day-js added to each package's dependency list. easy-day-js…

Socket
npm Package Uses Prompt Injection and Token Flooding to Disrupt AI Malware Scanners

npm Package Uses Prompt Injection and Token Flooding to Disrupt AI Malware Scanners

Last week, Socket Threat Research reported that newer Mini Shai-Hulud, Miasma, and Hades packages were embedding fake prompt-injection headers before obfuscated JavaScript payloads. Those comments did not affect runtime execution, but they appeared designed to interfere with AI-assisted malware review. Now we are seeing that same idea tested more directly in a package that appears designed to probe how AI-based scanners handle prompt injection, safety-triggering content, and context flooding.…

Socket
Introducing Manifest Alerts

Introducing Manifest Alerts

Socket now detects missing lockfiles with Manifest Alerts, a new kind of alert for supply chain risks found in project manifests. The feature was built in response to a real problem customers faced during the Axios npm compromise. Due to the complexities of modern dependency resolution, the blast radius of this incident was much wider than it initially appeared. Exposure was not limited to projects that directly depended on the compromised Axios version. For teams with committed lockfiles and…

Socket