Flux
Toutes les catégories

Cybersécurité

277 articles

Free Certified Patch for Critical Rails Active Storage Vulnerability

Free Certified Patch for Critical Rails Active Storage Vulnerability

Ruby on Rails has released security updates addressing 21 vulnerabilities, including a critical Active Storage flaw that could allow unauthenticated attackers to write arbitrary files to a server through crafted uploads. Under certain configurations, attackers may also be able to read sensitive files, potentially leading to remote code execution. Socket is releasing a free Certified Patch for the critical vulnerability, tracked as GHSA-f3w6-w445-fwh9 (CVSS 9.8). The patch is available to…

Socket
Shai-Hulud Descendant Surfaces in Malicious Ruby Gem That Steals Credentials and Poisons AI Tools

Shai-Hulud Descendant Surfaces in Malicious Ruby Gem That Steals Credentials and Poisons AI Tools

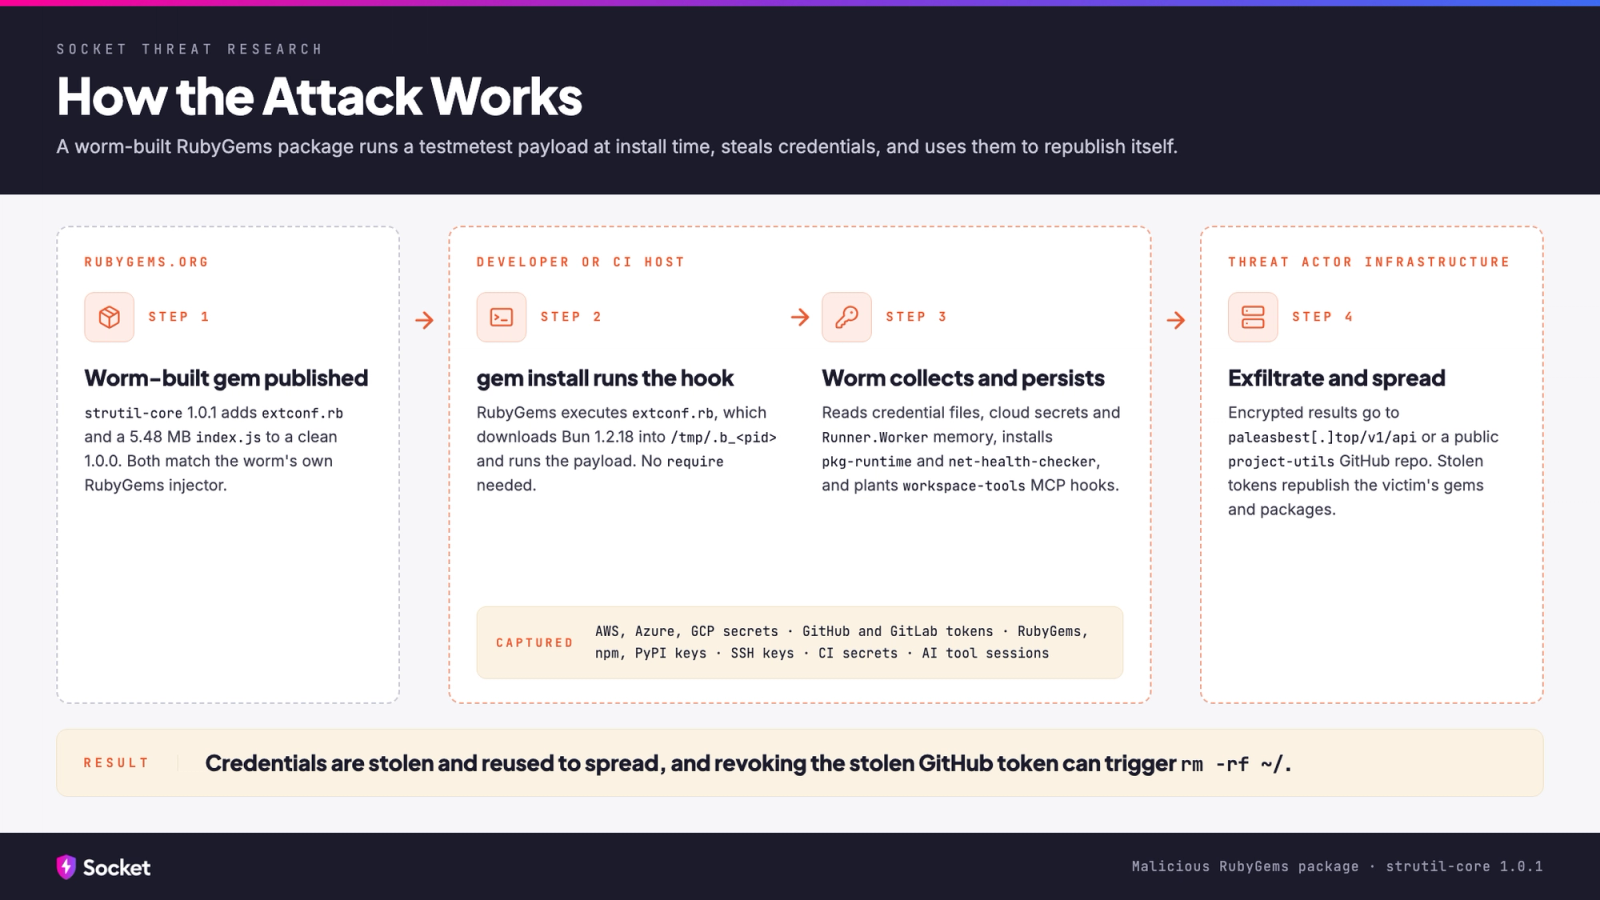
Socket’s Threat Research Team analyzed strutil-core version 1.0.1, a malicious RubyGems package that runs a 5.48 MB credential-stealing worm when it is installed. The RubyGems account jamnajiea published a clean 1.0.0 on November 1, 2026, and pushed the malicious 1.0.1 less than two hours later. Socket’s AI Scanner flagged it 70 seconds after publication, and RubyGems removed both versions about five hours after the malicious release. strutil-core was a standalone gem, not a compromised…

Socket
GitHub to Block pull_request_target Workflows by Default Starting December 2

GitHub to Block pull_request_target Workflows by Default Starting December 2

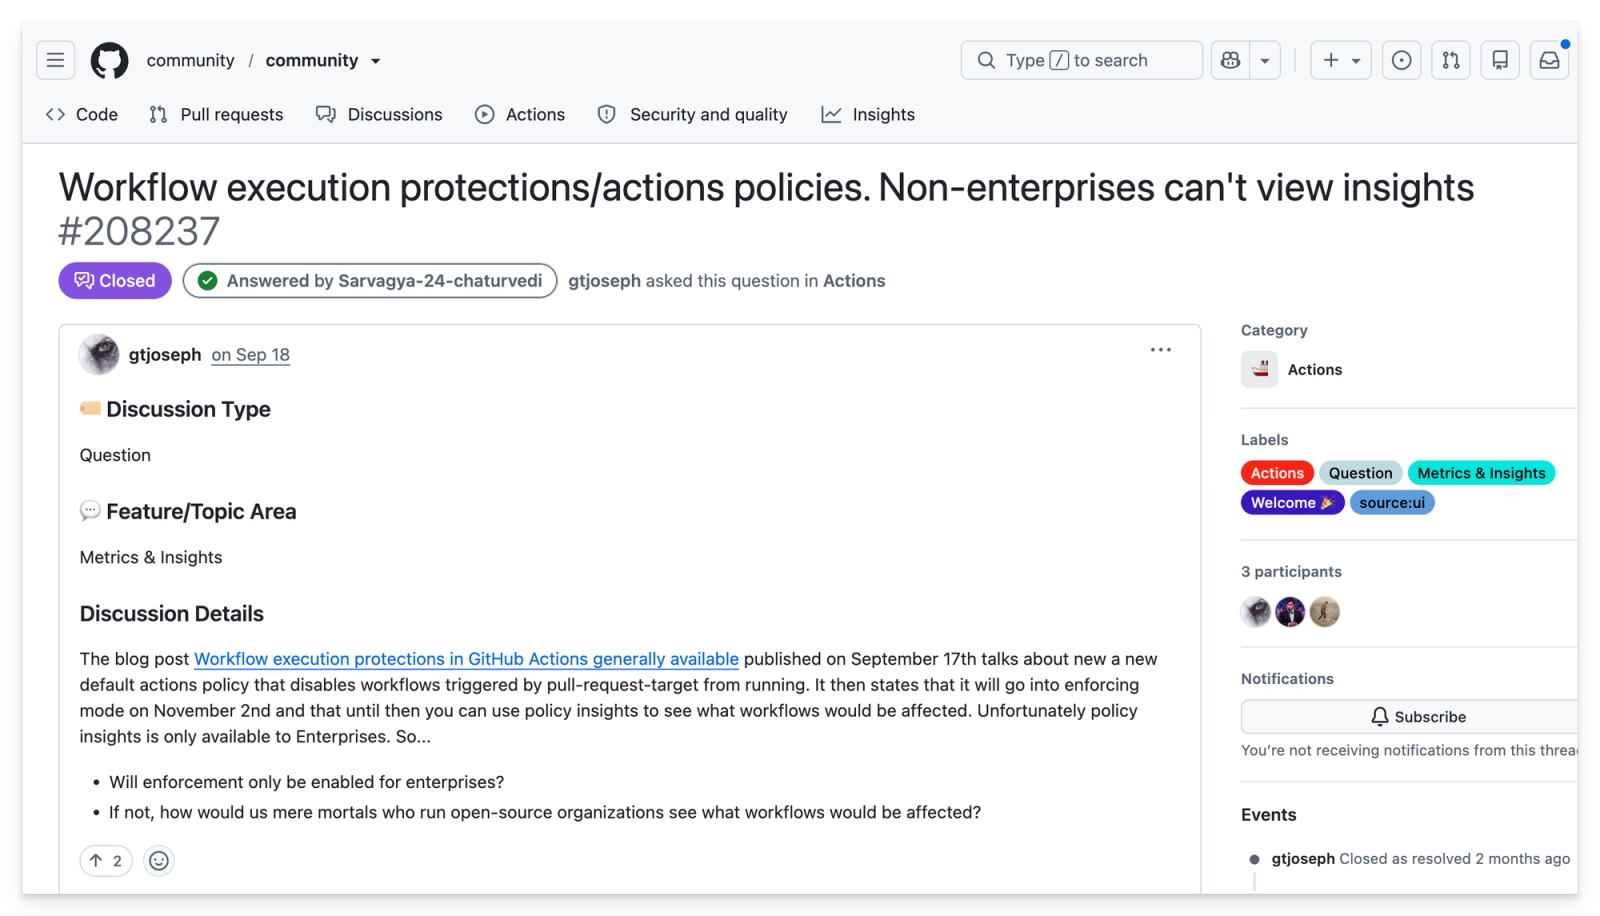
GitHub will begin blocking GitHub Actions workflows triggered by pull_request_target in public repositories on December 2, 2026, expanding its protections against a class of CI/CD vulnerabilities that has repeatedly enabled attackers to steal credentials and compromise open source software releases. The restriction, originally announced in September, will prevent affected workflows from running unless an applicable Actions event policy explicitly allows them. GitHub had initially scheduled…

Socket
Hardening GitHub Actions Against Outside Threats

Hardening GitHub Actions Against Outside Threats

The supply chain attacks that defined 2025 and 2026 did not arrive as typosquats or as newly published malicious packages. They arrived inside legitimate, widely installed packages whose maintainers wrote no malicious code. The malicious code entered during the release, and in most cases the release ran on GitHub Actions. Some of the better-known incidents on widely used projects, as a sample rather than a complete list: tj-actions/changed-files, March 2025 Nx s1ngularity, August 2025…

Socket
Composer 2.11 Adds Dependency Cooldowns

Composer 2.11 Adds Dependency Cooldowns

Composer 2.11 has introduced dependency cooldowns, giving PHP developers a native way to delay newly published package versions before they become eligible for installation. The release arrives nearly a year after developers first requested the feature, bringing Composer into line with package managers that have already adopted minimum release age policies to reduce exposure to supply chain attacks. The new config.policy.cooldown setting allows developers to specify a waiting period in hours,…

Socket
Cursor Removes Malicious Claude Code 2.1.313 Extension From Its Marketplace

Cursor Removes Malicious Claude Code 2.1.313 Extension From Its Marketplace

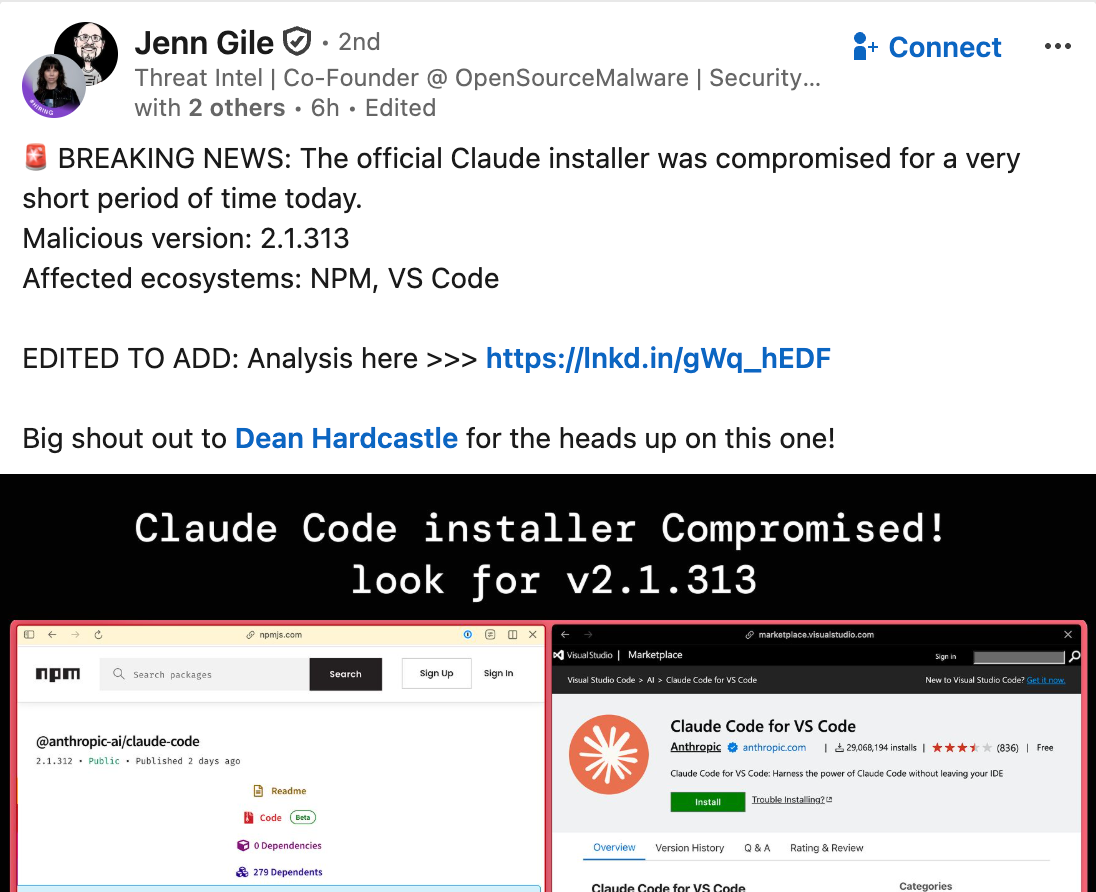
Cursor has confirmed that a malicious Claude Code extension labeled version 2.1.313 was available through its extension marketplace on October 29, potentially affecting up to 5,000 users. The disclosure identifies the distribution source behind a malware report initially attributed to Open VSX, where Socket’s investigation found no corresponding publication or removal records. OpenSourceMalware initially reported that a malicious version of Anthropic’s Claude Code extension, 2.1.313, was…

Socket
OpenCode User Hit with Hostile Backlash After Reporting Free AI Loophole

OpenCode User Hit with Hostile Backlash After Reporting Free AI Loophole

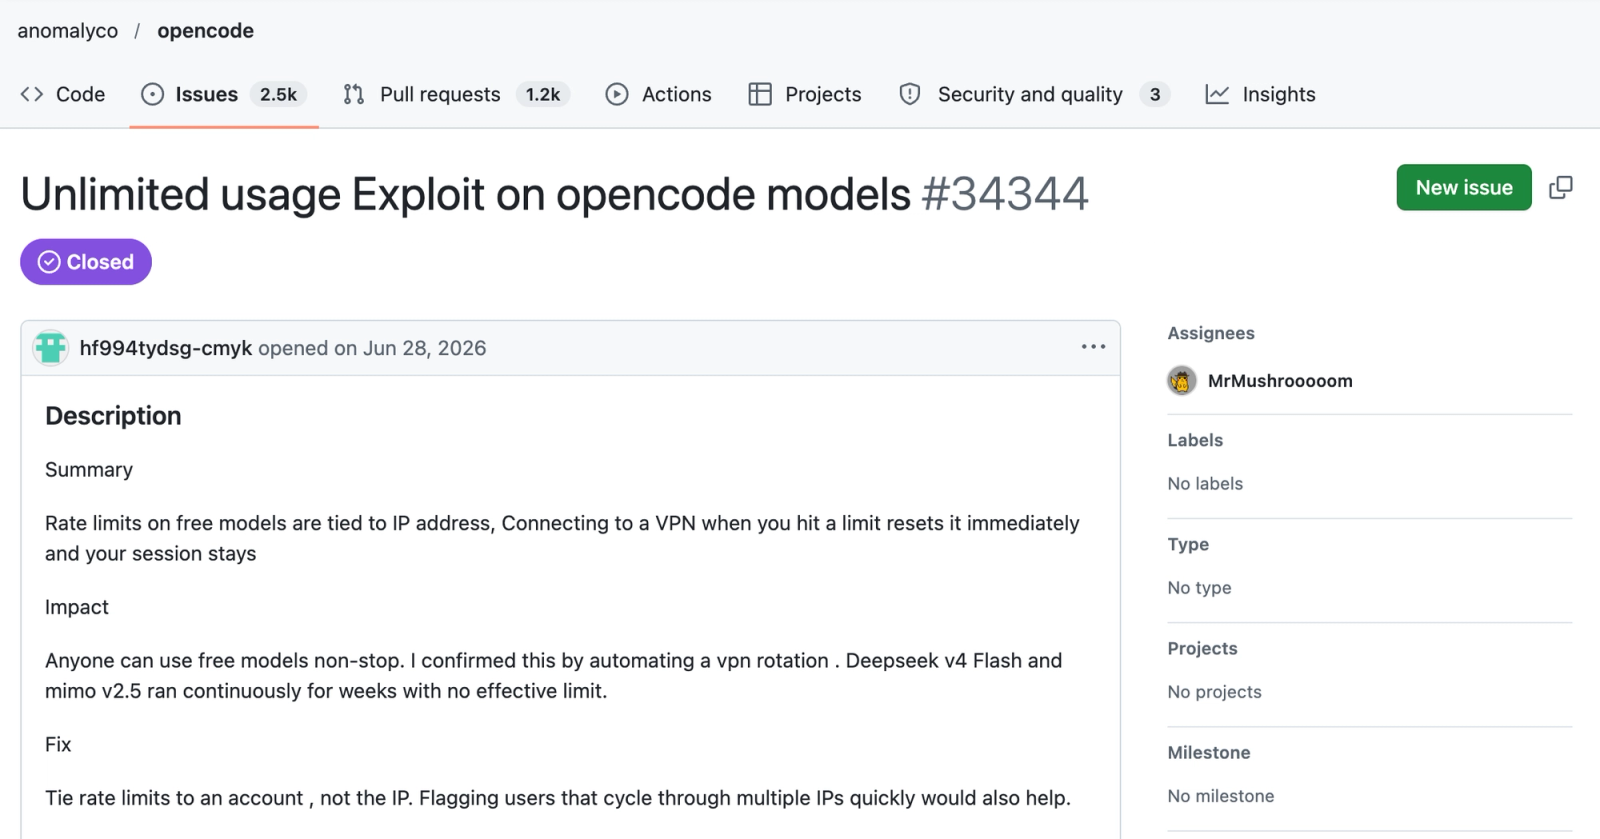
An OpenCode user who reported a loophole in its free AI usage limits became the target of harassment, including comments encouraging suicide, from people who blamed the disclosure for cutting off their supply of free AI. The GitHub thread has since been deleted, although an earlier version remains available through the Wayback Machine. OpenCode is an open source AI coding agent that helps developers write, edit, and run code from a terminal, IDE, or desktop app. The MIT-licensed software can…

Socket
Searchjacked: Hidden Browser Extensions Hijack Searches for 13 Million Users

Searchjacked: Hidden Browser Extensions Hijack Searches for 13 Million Users

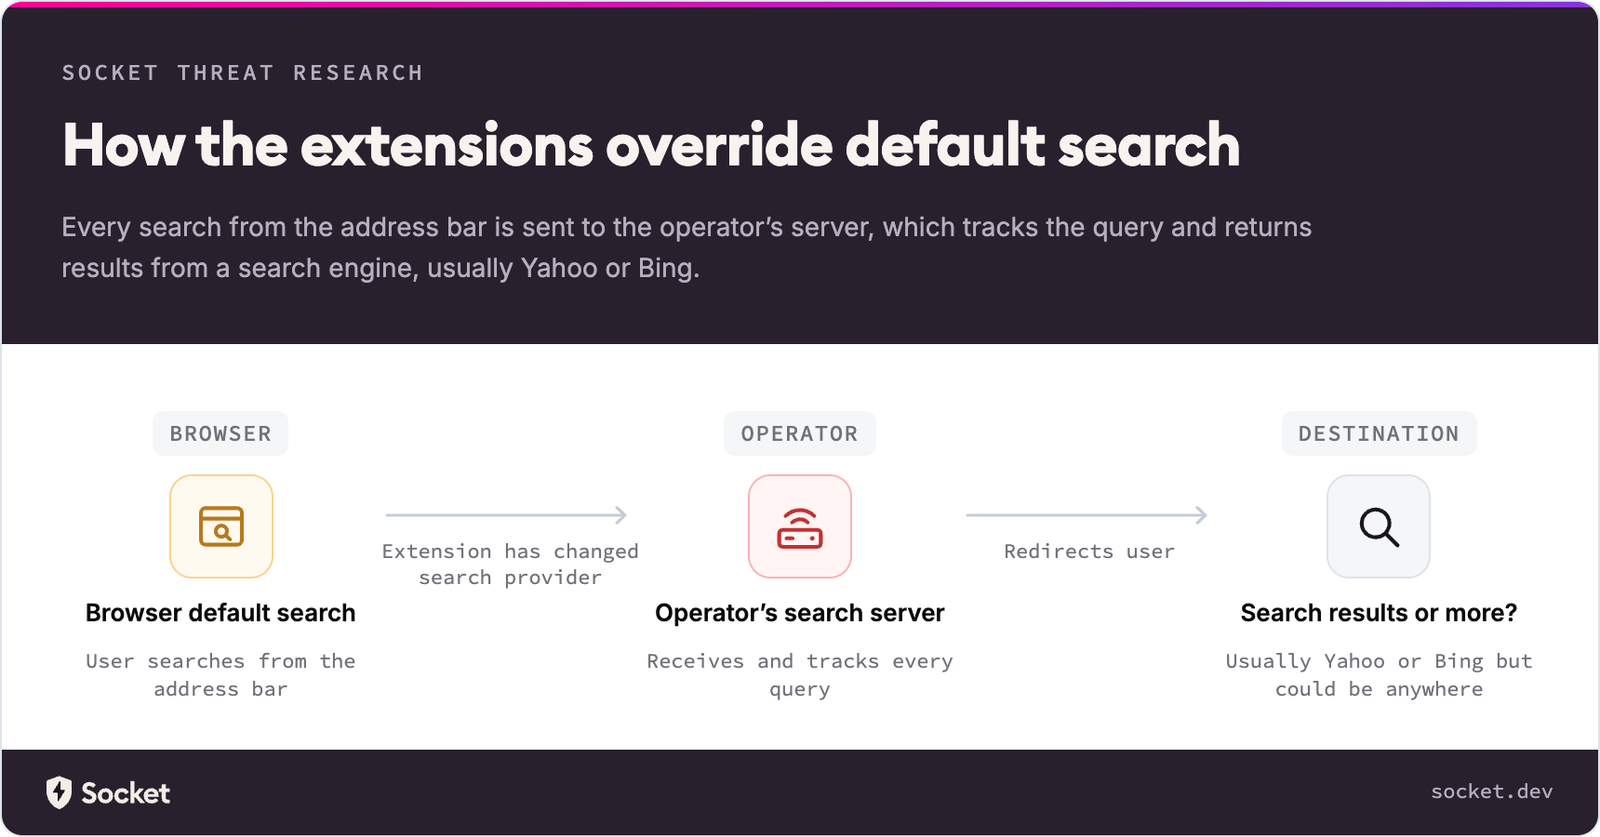
You may have come across ads on webpages promoting "manual finder", "safe search", "PDF converter", or "AI search" tools which often end up as easy to install browser extensions. What are these extensions actually doing and who is behind them? This investigation expands on previous research with 264 newly identified extensions which exist only to capture users search queries impacting 8.7 million more users. This brings the total number of distinct extensions to 319 installed by roughly 13.4…

Socket
Malicious Firefox Extensions Impersonate Phantom, Jupiter, and Bitget to Steal Wallet Secrets

Malicious Firefox Extensions Impersonate Phantom, Jupiter, and Bitget to Steal Wallet Secrets

Socket’s Threat Research Team identified a cluster of malicious Firefox extensions that impersonate well-known crypto wallets and steal recovery phrases and private keys. The extensions use Unicode homoglyphs to copy the names of Phantom, Jupiter, and Bitget, and they route stolen secrets to brand-named subdomains of a single command-and-control apex, bonto[.]io. Each signed package carries a complete, always-on stealer, so the malicious code is present in what Mozilla reviewed. The Phantom…

Socket
Socket Threat Intel Now Shows Which Malware Campaigns Were Blocked or Detected

Socket Threat Intel Now Shows Which Malware Campaigns Were Blocked or Detected

When a new malware campaign emerges, you need to know whether it reached your organization and whether your defenses stopped it. Socket Threat Intel now makes those answers easier to find, with campaign summaries that show what Socket blocked or detected and links to the scans and Firewall events behind them. Every malware campaign on the Threat Intel → Campaigns page now carries a real-time summary for your organization: Blocked by Socket, Detected in Firewall/SCA, or Not Detected. Each…

Socket
eMudhra, Brotli, and the Long Tail of a Security Fix

eMudhra, Brotli, and the Long Tail of a Security Fix

How much software do you have to update to fix one vulnerability, let alone two far-reaching ones in the same week? Our corner of the internet was getting impatient waiting for Node’s eMudhra fix to drop. The certificate block had merged, and we were ready to update Node, rebuild, and move on. Then the October 21 release dropped, and we got Brotli too. That covered both problems in Node. But how much else used that same decoder? It was tucked into other applications and runtimes, and now we had…

Socket
New Evidence Shows LiteLLM Secret-Stealing Workflows Ran 11 Days Before Supply Chain Attack

New Evidence Shows LiteLLM Secret-Stealing Workflows Ran 11 Days Before Supply Chain Attack

Socket's Threat Research team found that a malicious secret-exfiltration workflow was already running successfully in the BerriAI/litellm repository on October 10, 2026, eleven days before the release-pipeline attack that published malicious litellm==1.107.0 artifacts, placing observed malicious activity in the repository more than a week before the compromise came to light. What Socket Found # The compromise of the BerriAI/litellm release pipeline on October 21, 2026, which produced malicious…

Socket
Cloudflare Introduces a Faster TypeScript Compiler Written in Rust

Cloudflare Introduces a Faster TypeScript Compiler Written in Rust

Microsoft’s Go port of TypeScript’s compiler and tooling delivered roughly 10× faster type checking. Now Cloudflare is working on a Rust port of TypeScript’s compiler that promises even faster type checking and lower memory use. The TypeScript team is collaborating on the work, and some of the optimizations are already making their way into the official compiler. Cloudflare announced on October 20 that it is bringing tsrs, a Rust port of the TypeScript compiler, into its Oxc toolchain. Its…

Socket
PHP Foundation Says Chainguard Broke Security Embargo Ahead of Emergency Patches

PHP Foundation Says Chainguard Broke Security Embargo Ahead of Emergency Patches

The PHP Foundation says Chainguard broke a coordinated security embargo by releasing patched PHP container images hours ahead of schedule, making the fix available for attackers to study while other distributors were still preparing updates. In a postmortem published October 21, the Foundation described a disclosure process disrupted by leaked CVE identifiers, an accidentally published exploit demonstration, and Chainguard’s decision to release early. It also acknowledged that work on the…

Socket
PHP Patches Critical RCE Vulnerabilities, Organizations Urged to Take Unpatched Sites Offline

PHP Patches Critical RCE Vulnerabilities, Organizations Urged to Take Unpatched Sites Offline

Organizations running internet-facing PHP applications have been advised to take them offline if they cannot immediately patch two critical vulnerabilities. That is how bad this is: the NSA recommended taking affected systems offline until they can be fully mitigated, while CERT-EU urged organizations unable to patch to consider isolating their applications from public networks. The patches are now available. PHP released emergency updates on October 21, fixing flaws that can let attackers…

Socket