Avoir son ASN personnel pour annoncer ses IPs sur Internet
Avoir son ASN personnel pour annoncer ses IPs sur Internet
Comment j'ai obtenu mon propre ASN et utilisé BGP pour annoncer des routes IPv6 depuis chez moi.
Lire
Comment j'ai obtenu mon propre ASN et utilisé BGP pour annoncer des routes IPv6 depuis chez moi.
Un onduleur sans supervision, ça ne protège qu'à moitié. NUT connecté à Proxmox via Synology : monitoring en temps réel et arrêt automatique en cas de coupure.

Les solutions RAID classiques gaspillent de l’espace lorsque les disques sont de tailles différentes. Le RAID logiciel Linux avec LVM exploite la capacité totale de chaque disque et permet d’étendre le stockage en remplaçant un ou deux disques à la fois.1 Nous partons de quatre disques de taille identique : $ lsblk -Mo NAME,TYPE,SIZE NAME TYPE SIZE vda disk 101M vdb disk 101M vdc disk 101M vdd disk 101M Nous créons une partition sur chacun d’eux : $ sgdisk --zap-all --new=0:0:0 -t 0:fd00…
Ce mois-ci : scan de vulnérabilités, monitoring uptime, suivi des mises à jour Linux, documentation statique et un magazine scientifique à découvrir.
Bloquer l'accès Internet d'un objet connecté ou d'un appareil enfant avec UniFi Network : méthode mise à jour, compatible IPv4 et IPv6.
Akvorado collecte des flux sFlow et IPFIX via UDP. Comme UDP ne retransmet pas les paquets perdus, il faut les traiter rapidement. Akvorado exécute plusieurs routines écoutant sur le même port. Le noyau devrait répartir équitablement les paquets reçus entre ces routines. Cependant, cela ne fonctionne pas comme prévu. Quelques routines présentent une perte de paquets importante : $ curl -s 127.0.0.1:8080/api/v0/inlet/metrics \ > | sed -n s/akvorado_inlet_flow_input_udp_in_dropped//p…
Part one of this series covered attackers with no credential for your organization, who reach the pipeline through a pull request, a dependency or a third-party action. Those controls are largely deterministic. Pin an action to a commit SHA and a retagged action cannot run. This post covers the other half, and it behaves differently. Here the attacker presents a valid credential. Either a maintainer's account, token or session has been stolen, or a person with legitimate access is acting…
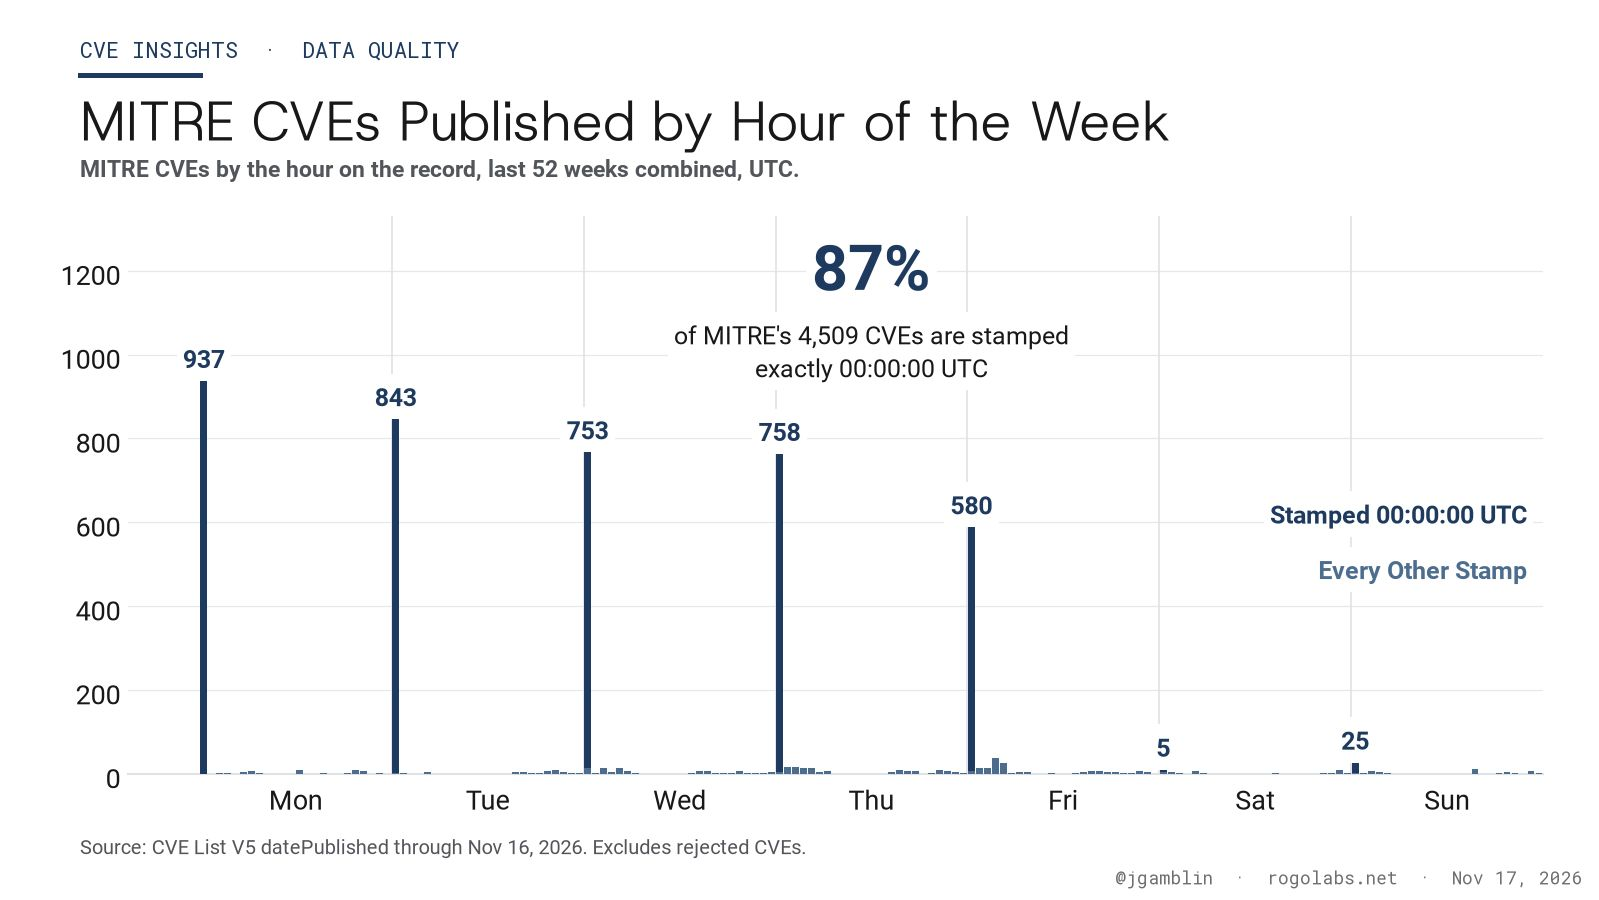
MITRE has acknowledged that a legacy publishing system is responsible for inaccurate timestamps in thousands of CVE records, following research showing that 87% of the organization's CVEs published over the past year were assigned a publication time of exactly midnight UTC. MITRE says the legacy system responsible for the problem will be phased out in the first quarter of 2027. The findings come from security researcher Jerry Gamblin, founder of RogoLabs, an independent open source research lab…
An attacker exploited a vulnerability in Optimizely's Web Experimentation platform on November 16, 2026, distributing malicious JavaScript through websites operated by some of the world's largest brands. Security researcher Scott Helme of Report URI identified 188 infected JavaScript snippets associated with 178 organizations, including the BBC, CNN, Zoom, GitLab, IKEA, and HSBC. The attack exposed website visitors to malware designed to replace cryptocurrency wallet addresses, steal payment…
Executive Summary # The Microsoft agent-framework PyPI package was compromised on November 17th, affecting versions 1.26.1 and 1.26.2. Both versions install Python startup hooks that silently collect credentials, environment data, and cloud identity tokens, then exfiltrate them to a webhook[.]site endpoint. Avoid installing either version; if installed, remove them and rotate potentially exposed credentials. Attack Analysis # On Python startup, the .pth file imports a module that launches…
pnpm has introduced an experimental lockfile format designed to reduce Git merge conflicts by changing how dependency relationships are recorded. The new format, available starting with pnpm 12.19.0, previews changes planned for pnpm 13 and is available as an opt-in setting. The change addresses a common frustration in JavaScript development, particularly in projects with multiple contributors or large dependency trees. Updates to dependencies can produce substantial changes in pnpm-lock.yaml,…
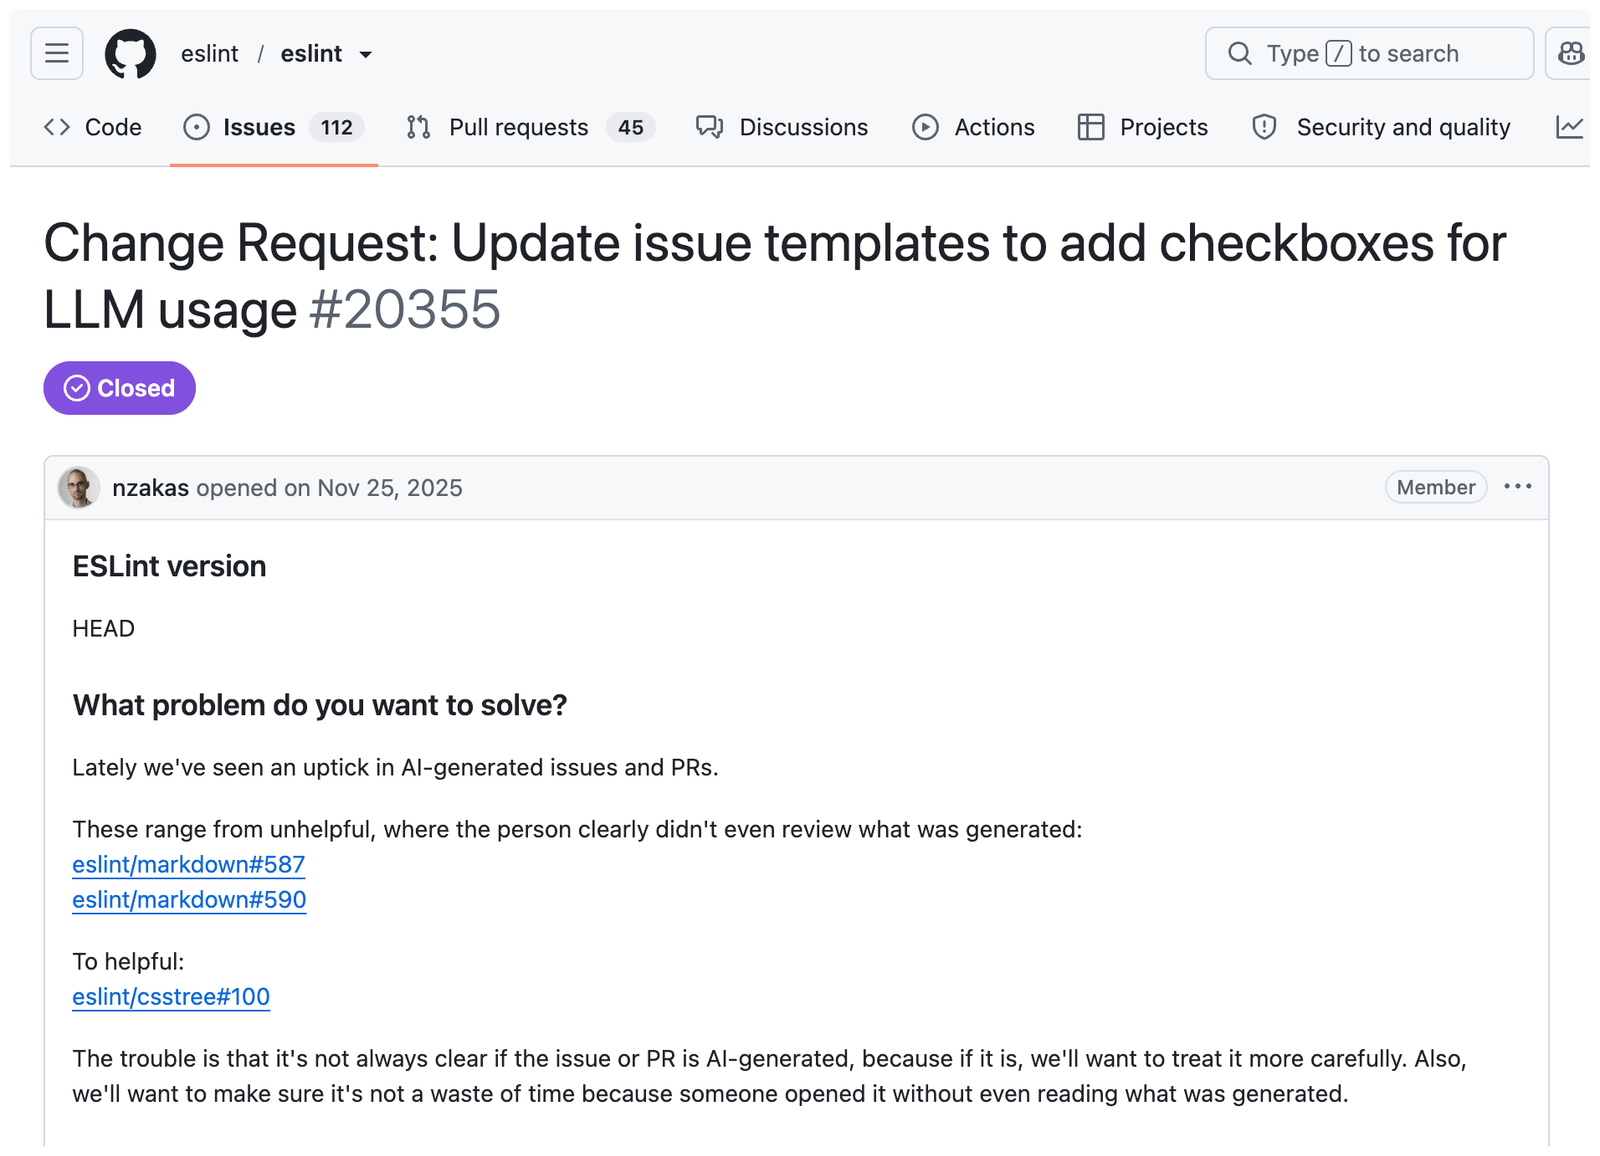
ESLint is retiring its contributor pool after five years, citing growing difficulties with AI-generated contributions and disputes over whether contributors deserved payment for work produced with AI assistance. In a November 13 announcement, ESLint creator Nicholas C. Zakas said the program had paid outside contributors more than $51,000 and helped recruit several future team members. But the increasing volume of AI-generated issues and pull requests, along with accusations about undisclosed…
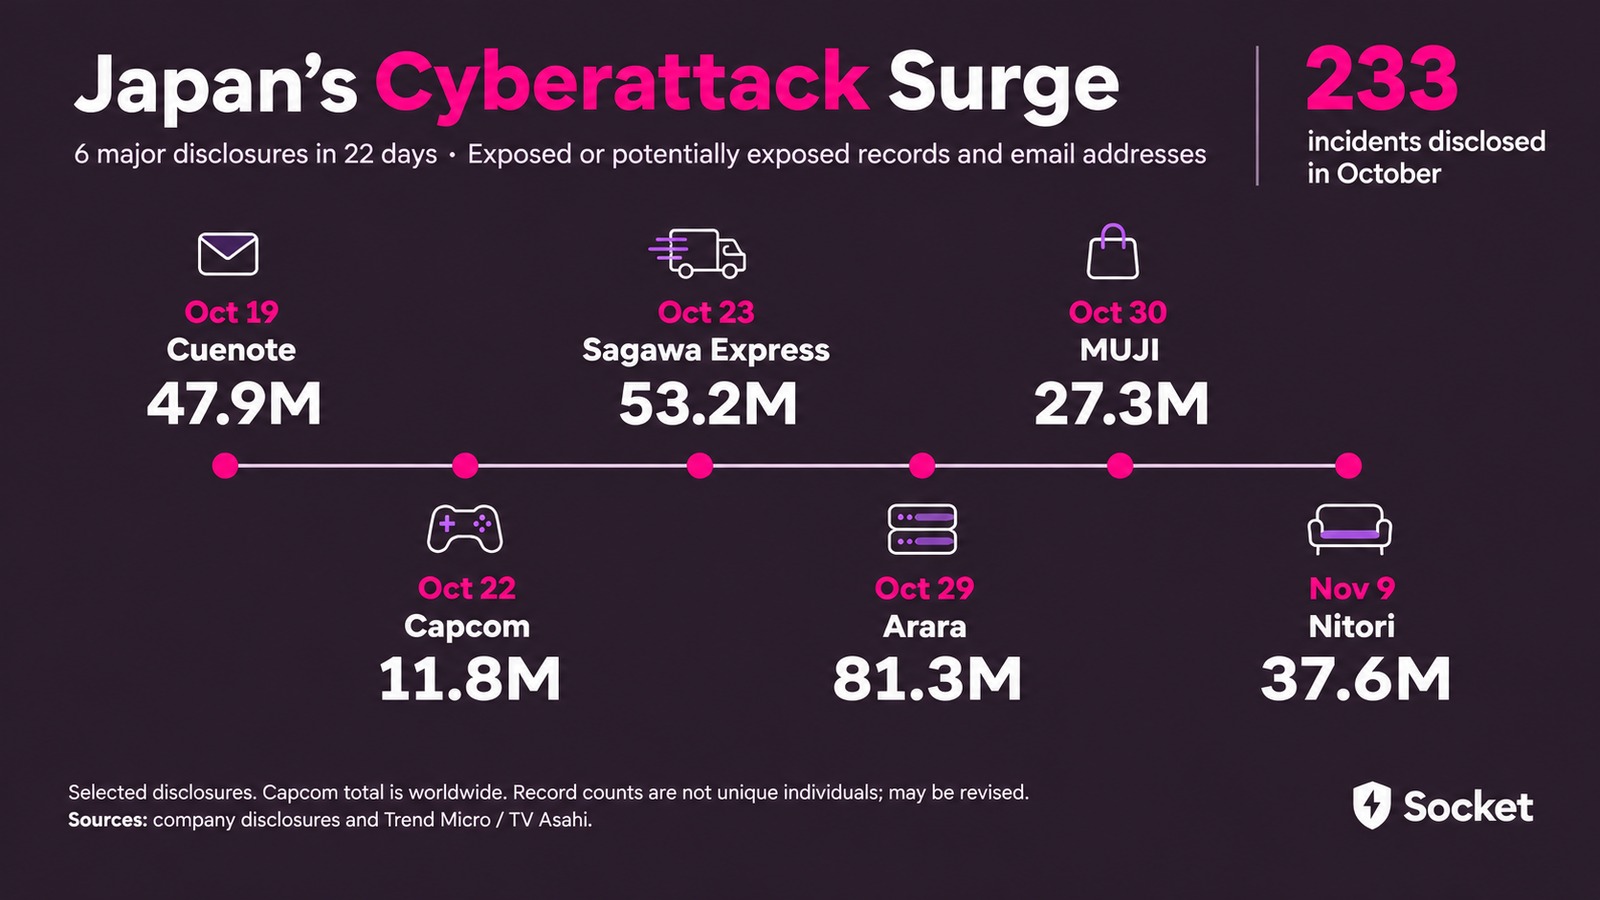
Japan is facing an extraordinary surge in cyberattacks, with a record 233 security incidents publicly disclosed in October alone. That's roughly 2.4 times the previous monthly record, according to Trend Micro data reported by TV Asahi. Cyberattacks are rising around the world, but the pace of disclosures in Japan is staggering. Nearly every day has dragged another affected company, service provider, or public institution into the headlines. The volume of exposed information is growing even…
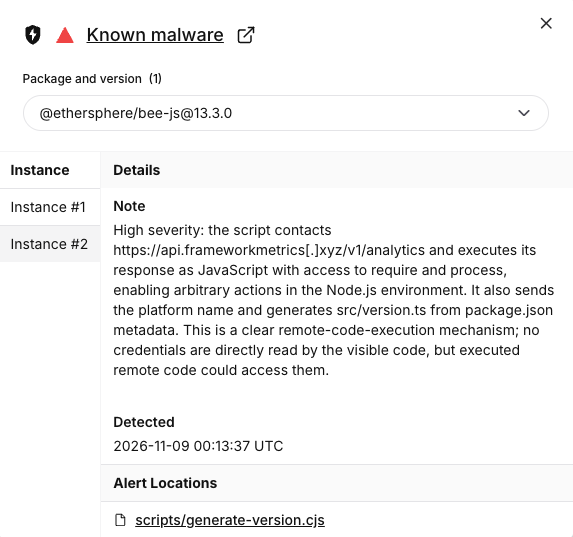
Socket’s Threat Research Team analyzed the November 9, 2026 compromise of Ethersphere’s release pipeline, in which a threat actor used the project’s own GitHub automation to publish a malicious @ethersphere/bee-js 13.3.0 to npm and a trojanized Swarm Desktop 0.56.2 release on GitHub. Both artifacts carry a small loader that fetches JavaScript from api[.]frameworkmetrics[.]xyz and executes it with full Node.js privileges. The Ethereum smart contract that tells the later stages where to connect,…